

This website stores cookies on your computer. These cookies are used to improve your website experience and provide more personalized services to you, both on this website and through other media. To find out more about the cookies we use, see our privacy policy.
Secure Every Workload.Govern Every Dollar.
We build the security controls, governance frameworks, and financial guardrails that keep your cloud protected, compliant, and cost-efficient at every stage of growth.
Our Approach
Protection and profitability, governed as one.
Security gaps and cost overruns share the same root causes: limited visibility, inconsistent controls, and unclear ownership. We address both through a single governance model that is enforced automatically, measured continuously, and owned clearly.
Gain Visibility
We inventory every asset, identity, and dollar of spend across your cloud estate, so every decision rests on facts.
Define the Guardrails
Security standards, compliance obligations, and budget policies are translated into precise, enforceable rules.
Enforce Through Automation
Policy as code, automated remediation, and cost controls apply your guardrails consistently, without slowing your teams down.
Improve Continuously
Regular posture reviews, anomaly detection, and optimization cycles keep risk low and value high as your environment evolves.
Our Services
Cloud Security and Cost Governance Services
End-to-end control over the risk and spend of your cloud environment.
Cloud Security & Governance
End-to-end control over the risk and spend of your cloud environment.
8 platformsCloud Security Posture Management
CSPM & DetectionContinuously detect misconfigurations, exposed resources, and policy violations across AWS, Azure, and Google Cloud. Prioritize and remediate risks before they become incidents.
Identity and Access Governance
IAM & Least PrivilegeEnforce least-privilege access, strong authentication, and privileged access controls. Reduce the risk of credential misuse and excessive permissions.
Data Protection and Encryption
Data Security & KMSClassify sensitive data, manage encryption keys, and secure information at rest and in transit. Protect critical assets and meet your data protection obligations.
Compliance and Regulatory Readiness
Audit ReadinessMap cloud controls to frameworks such as ISO 27001, SOC 2, PCI DSS, HIPAA, and GDPR, with automated evidence collection. Shorten audit cycles and stay continuously audit-ready.
Threat Detection and Incident Response
Detection & ResponseCentralize logging, detect anomalies, and establish tested response playbooks. Contain threats faster and limit the impact on your business.
Policy as Code and Cloud Governance
Policy as CodeCodify guardrails, tagging standards, and account structures with automated enforcement. Ensure every deployment meets policy from the first commit.
FinOps and Cloud Cost Optimization
FinOps & OptimizationRightsize resources, optimize commitment-based discounts, and eliminate idle spend. Lower your cloud bill while protecting performance.
Cost Visibility, Budgeting, and Chargeback
Cost AllocationAllocate spend by team, product, and environment with budgets, forecasts, and anomaly alerts. Build accountability and achieve predictable cloud spend.
Ready to Secure and Optimize Your Cloud?
Protect critical workloads, ensure continuous compliance, and eliminate wasteful cloud spend.
The Governance Lifecycle: Turning Risk and Spend into Managed Outcomes
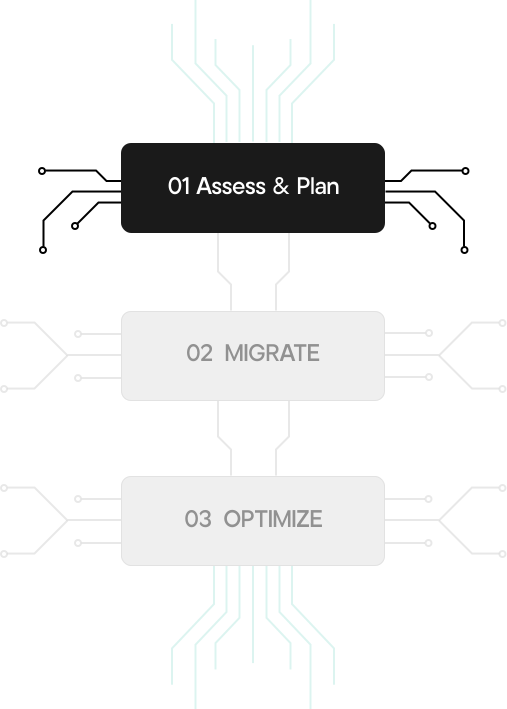
01
Assess & Prioritize
Establish a clear security and financial baseline.
Review security posture, access models, compliance gaps, and spend patterns to establish a clear baseline.
Focus effort where it delivers maximum impact.
Rank risks and savings opportunities by business impact, so effort goes where it delivers the most value.
02
Implement & Automate
Deploy controls and governance mechanisms.
Deploy security controls, governance policies, monitoring, and cost mechanisms across your cloud environments.
Codify guardrails into pipelines and services.
Encode policies and remediation into pipelines and platform services for consistent, hands-off enforcement.
03
Monitor & Optimize
Real-time posture and spend tracking.
Track posture, compliance, and spend in real time through dashboards, alerts, and regular executive reporting.
Refine controls and financial commitments.
Refine controls and commitments over time, so protection keeps strengthening and costs keep improving.
Our Partners
Trusted Technologies, Proven Practices
We work with leading cloud providers, security platforms, and FinOps tooling, applying certified best practices to protect and optimize your environment.
01 / GCP

Advanced Tier Partner
Google Cloud
As an AWS partner, we apply proven best practices for secure, high-performing, cost-efficient architectures. AWS programs and tooling help us modernize faster and cut operational overhead.
- GKE & Anthos
- BigQuery & Looker
- Cloud Run
- Apigee Integration
02 / Azure

Solutions Partner
Microsoft Azure
Our Microsoft partnership unlocks Azure best practices, optimization frameworks, licensing benefits, and adoption programs. You transform faster and keep financial control.
- AKS & Arc
- Landing Zones
- Azure DevOps
- Synapse & Fabric
03 / AWS

Advanced Tier Partner
Amazon Web Services
Deep expertise in Google Cloud's native services, cost governance, and security controls lets you standardize operations and optimize consistently across distributed environments.
- EKS & Fargate
- Migration Hub
- Well-Architected
- Control Tower
01. BLOG
How Automation Can Reduce Administrative Work Across Departments
Automate repetitive administrative tasks, improve workflow efficiency, reduce errors, and boost productivity across HR, finance, sales, and operations.
READ MOREInterested In Learning More?
You can find relevant information about our company and services by browsing through the following FAQs. Please get in touch with us for more details.
01
What is cloud security and cost governance?
Cloud security and cost governance is the combined practice of protecting cloud environments and controlling cloud spend through consistent policies, monitoring, and accountability. It reduces security risk, supports regulatory compliance, and ensures your cloud investment delivers measurable business value.
02
Why should cloud security and cost governance be managed together?
Both depend on the same foundations: complete visibility, consistent tagging, clear ownership, and automated policy enforcement. Managing them together removes duplicated effort and exposes issues that overlap, such as forgotten resources that create both security exposure and unnecessary cost.
03
What is cloud security posture management?
Cloud security posture management (CSPM) is the continuous monitoring of cloud configurations against security best practices and compliance standards. It identifies misconfigurations, excessive permissions, and exposed resources, then guides or automates remediation before attackers can exploit them.
04
What is the shared responsibility model in cloud security?
The shared responsibility model divides security duties between the cloud provider and the customer. Providers secure the underlying infrastructure, while customers remain responsible for their data, identities, configurations, and workloads. Understanding this boundary is essential for closing security gaps.
05
What are the most common cloud security risks?
Common risks include misconfigured storage and services, excessive access permissions, weak identity controls, unpatched workloads, insecure APIs, and unmanaged shadow resources. A governance program addresses these through continuous monitoring, least-privilege access, and automated policy enforcement.
06
How do you maintain compliance with GDPR, HIPAA, and PCI DSS in the cloud?
Compliance is maintained by mapping regulatory requirements to specific technical controls, enforcing them through policy as code, and collecting evidence automatically. Continuous monitoring flags deviations early, which keeps you audit-ready throughout the year rather than only at audit time.
07
What is policy as code?
Policy as code expresses security, compliance, and cost rules as machine-readable code that is version-controlled and enforced automatically. It blocks non-compliant deployments, applies standards uniformly across accounts, and creates a clear audit trail of every policy change.
08
What is FinOps?
FinOps is a cloud financial management discipline that brings engineering, finance, and business teams together to manage cloud spend. It focuses on visibility, accountability, and optimization, so every team understands what it spends and why.